

CompTIA Security+ SY0-601 Practice Test Engine: Try These 463 Exam Questions
Guaranteed Success in CompTIA Security+ SY0-601 Exam Dumps
CompTIA Security+ SY0-601 Practice Test Questions, CompTIA Security+ SY0-601 Exam Practice Test Questions
CompTIA SY0-601 is the new version of the qualifying exam for the Security+ certification. This is the first security certificate that a candidate needs to earn in the field of information security. It validates the core knowledge required for any cybersecurity job and acts as the springboard to the mid-level cybersecurity positions.
NEW QUESTION 160
The Chief Executive Officer (CEO) of an organization would like staff members to have the flexibility to work from home anytime during business hours, incident during a pandemic or crisis, However, the CEO is concerned that some staff members may take advantage of the of the flexibility and work from high-risk countries while on holidays work to a third-party organization in another country. The Chief information Officer (CIO) believes the company can implement some basic to mitigate the majority of the risk. Which of the following would be BEST to mitigate CEO's concern? (Select TWO).
- A. Geolocation
- B. Certificates
- C. Time-of-day restrictions
- D. Role-based access controls
- E. Tokens
- F. Geotagging
Answer: A,F
NEW QUESTION 161
An end user reports a computer has been acting slower than normal for a few weeks. During an investigation, an analyst determines the system is sending the user's email address and a ten-digit number to an IP address once a day. The only recent log entry regarding the user's computer is the following:
Which of the following is the MOST likely cause of the issue?
- A. Ransomware is communicating with a command-and-control server.
- B. A bot on the computer is brute forcing passwords against a website
- C. The end user purchased and installed a PUP from a web browser
- D. A hacker is attempting to exfiltrate sensitive data
Answer: C
NEW QUESTION 162
After a phishing scam for a user's credentials, the red team was able to craft a payload to deploy on a server. The attack allowed the installation of malicious software that initiates a new remote session. Which of the following types of attacks has occurred?
- A. Application programming interface
- B. Privilege escalation
- C. Session replay
- D. Directory traversal
Answer: B
NEW QUESTION 163
A researcher has been analyzing large data sets for the last ten months. The researcher works with colleagues from other institutions and typically connects via SSH to retrieve additional data. Historically, this setup has worked without issue, but the researcher recently started getting the following message:
Which of the following network attacks is the researcher MOST likely experiencing?
- A. MAC cloning
- B. Man-in-the-middle
- C. ARP poisoning
- D. Evil twin
Answer: B
NEW QUESTION 164
Which of the following holds staff accountable while escorting unauthorized personnel?
- A. Cameras
- B. Locks
- C. Visitor logs
- D. Badges
Answer: D
NEW QUESTION 165
Given the following logs:
Which of the following BEST describes the type of attack that is occurring?
- A. Password spraying
- B. Rainbow table
- C. Pass-the-hash
- D. Dictionary
Answer: A
NEW QUESTION 166
While checking logs, a security engineer notices a number of end users suddenly downloading files with the
.tar.gz extension. Closer examination of the files reveals they are PE32 files. The end users state they did not initiate any of the downloads. Further investigation reveals the end users all clicked on an external email containing an infected MHT file with an href link a week prior. Which of the following is MOST likely occurring?
- A. A RAT was installed and is transferring additional exploit tools.
- B. A logic bomb was executed and is responsible for the data transfers.
- C. A fireless virus is spreading in the local network environment.
- D. The workstations are beaconing to a command-and-control server.
Answer: A
Explanation:
Explanation
https://www.howtogeek.com/362203/what-is-a-tar.gz-file-and-how-do-i-open-it/
NEW QUESTION 167
A network administrator has been alerted that web pages are experiencing long load times. After determining it is not a routing or DNS issue, the administrator logs in to the router, runs a command, and receives the following output:
Which of the following is the router experiencing?
- A. Buffer overflow
- B. DDoS attack
- C. Resource exhaustion
- D. Memory leak
Answer: C
NEW QUESTION 168
Select the appropriate attack and remediation from each drop-down list to label the corresponding attack with its remediation.
INSTRUCTIONS
Not all attacks and remediation actions will be used.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Answer:
Explanation:
NEW QUESTION 169
If a current private key is compromised, which of the following would ensure it cannot be used to decrypt all historical data?
- A. Key stretching
- B. Homomorphic encryption
- C. Perfect forward secrecy
- D. Elliptic-curve cryptography
Answer: B
NEW QUESTION 170
A security analyst is running a vulnerability scan to check for missing patches during a suspected security rodent During which of the following phases of the response process is this activity MOST likely occurring?
- A. Containment
- B. Preparation
- C. Identification
- D. Recovery
Answer: C
NEW QUESTION 171
A security analyst is reviewing the output of a web server log and notices a particular account is attempting to transfer large amounts of money:
Which of the following types of attack is MOST likely being conducted?
- A. API
- B. Session replay
- C. SQLi
- D. CSRF
Answer: B
NEW QUESTION 172
A root cause analysis reveals that a web application outage was caused by one of the company's developers uploading a newer version of the third-party libraries that were shared among several applications. Which of the following implementations would be BEST to prevent the issue from reoccurring?
- A. Automated failover
- B. SWG
- C. CASB
- D. Containerization
Answer: D
Explanation:
Containerization is defined as a form of operating system virtualization, through which applications are run in isolated user spaces called containers, all using the same shared operating system (OS).
NEW QUESTION 173
A security analyst receives a SIEM alert that someone logged in to the appadmin test account, which is only used for the early detection of attacks. The security analyst then reviews the following application log:
Which of the following can the security analyst conclude?
- A. A replay attack is being conducted against the application.
- B. A credentialed vulnerability scanner attack is testing several CVEs against the application.
- C. An injection attack is being conducted against a user authentication system.
- D. A service account password may have been changed, resulting in continuous failed logins within the application.
Answer: D
NEW QUESTION 174
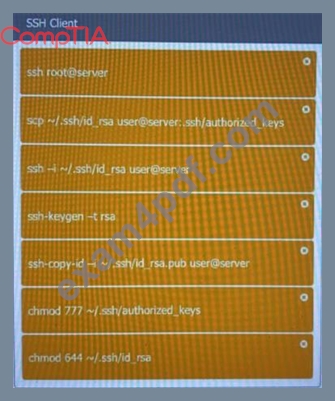
A security engineer is setting up passwordless authentication for the first time.
INSTRUCTIONS
Use the minimum set of commands to set this up and verify that it works. Commands cannot be reused.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Answer:
Explanation:
NEW QUESTION 175
Select the appropriate attack and remediation from each drop-down list to label the corresponding attack with its remediation.
INSTRUCTIONS
Not all attacks and remediation actions will be used.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Answer:
Explanation:

NEW QUESTION 176
An organization recently acquired an ISO 27001 certification. Which of the following would MOST likely be considered a benefit of this certification?
- A. It provides complimentary training and certification resources to IT security staff.
- B. It assures customers that the organization meets security standards
- C. It certifies the organization can work with foreign entities that require a security clearance
- D. It provides insurance in case of a data breach
- E. It allows for the sharing of digital forensics data across organizations
Answer: B
Explanation:
According to the ISO https://www.iso.org/standard/54534.html
ISO/IEC 27001:2013 specifies the requirements for establishing, implementing, maintaining and continually improving an information security management system within the context of the organization. It also includes requirements for the assessment and treatment of information security risks tailored to the needs of the organization. The requirements set out in ISO/IEC 27001:2013 are generic and are intended to be applicable to all organizations, regardless of type, size or nature.
NEW QUESTION 177
A retail executive recently accepted a job with a major competitor. The following week, a security analyst reviews the security logs and identifies successful logon attempts to access the departed executive's accounts. Which of the following security practices would have addressed the issue?
- A. Least privilege
- B. A non-disclosure agreement
- C. Offboarding
- D. An acceptable use policy
Answer: C
NEW QUESTION 178
A malicious actor recently penetration a company's network and moved laterally to the datacenter. Upon investigation, a forensics firm wants to know was in the memory on the compromised server. Which of the following files should be given to the forensics firm?
- A. Application
- B. Syslog
- C. Security
- D. Dump
Answer: D
Explanation:
Dump files are a special type of files that store information about your computer, the software on it, and the data loaded in the memory when something bad happens. They are usually automatically generated by Windows or by the apps that crash, but you can also manually generate them https://www.digitalcitizen.life/view-contents-dump-file/
NEW QUESTION 179
During an incident response, a security analyst observes the following log entry on the web server.
Which of the following BEST describes the type of attack the analyst is experience?
- A. SQL injection
- B. Directory traversal
- C. Cross-site scripting
- D. Pass-the-hash
Answer: C
NEW QUESTION 180
Select the appropriate attack and remediation from each drop-down list to label the corresponding attack with its remediation.
INSTRUCTIONS
Not all attacks and remediation actions will be used.
If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
Answer:
Explanation:

NEW QUESTION 181
A security engineer has enabled two-factor authentication on all workstations. Which of the following approaches are the MOST secure? (Select TWO).
- A. Password and voice
- B. Password and CAPTCHA
- C. Password and one-time token
- D. Password andsmart card
- E. Password and security question
- F. Password and fingerprint
Answer: D,F
NEW QUESTION 182
Which of the following will MOST likely adversely impact the operations of unpatched traditional programmable-logic controllers, running a back-end LAMP server and OT systems with human-management interfaces that are accessible over the Internet via a web interface? (Choose two.)
- A. SQL injection
- B. Cross-site scripting
- C. Poor system logging
- D. Weak encryption
- E. Server-side request forgery
- F. Data exfiltration
Answer: D,E
NEW QUESTION 183
A user reports constant lag and performance issues with the wireless network when working at a local coffee shop. A security analyst walks the user through an installation of Wireshark and get a five-minute pcap to analyze. The analyst observes the following output:
Which of the following attacks does the analyst MOST likely see in this packet capture?
- A. Bluejacking
- B. Session replay
- C. ARP poisoning
- D. Evil twin
Answer: D
NEW QUESTION 184
Aglobal pandemic is forcing a private organization to close some business units and reduce staffing at others.
Which of the following would be BEST to help the organization's executives determine the next course of action?
- A. Acommunications plan
- B. A disaster recovery plan
- C. An incident response plan
- D. A business continuity plan
Answer: D
NEW QUESTION 185
......
Study Tips
Passing the CompTIA SY0-601 exam is not an easy journey, but the benefits that it brings to your career worth every effort you put in the preparation process. You can equip yourself with the knowledge and skills required to attempt the certification test using different study materials. The experts recommend the use of exam dumps and practice tests as the most effective preparation options. Braindumps contain the past questions and answers to help you get an insight into the exam format and structure. This will improve your confidence so that you can face the real SY0-601 without any stress. Practice tests will also enable you to evaluate your current level of readiness and reveal your weak areas that still need your attention.
Test Engine to Practice SY0-601 Test Questions: https://www.exam4pdf.com/SY0-601-dumps-torrent.html
CompTIA SY0-601 Daily Practice Exam New 2021 Updated 463 Questions: https://drive.google.com/open?id=1uJTEcHc-7a3WE_c0mT0sIGuO_2G833c1
