

[Jul 28, 2025] MS-102 Test Prep Training Practice Exam Questions Practice Tests
Exam Questions Answers Braindumps MS-102 Exam Dumps PDF Questions
NEW QUESTION # 185
Your company has a Microsoft 365 subscription that uses an Azure AD tenant named contoso.com. The tenant contains the users shown in the following table.
You create a retention label named Label 1 that has the following configurations:
* Retains content for five years
* Automatically deletes all content that is older than five years
You turn on Auto labeling for Label1 by using a policy named Policy1. Policy1 has the following configurations:
* Applies to content that contains the word Merger
* Specifies the OneDrive accounts and SharePoint sites locations
You run the following command.
Set-RetentionConpliancePolicy Policy1 -RestrictiveRetention Strue -Force For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 186
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
You enable self-service password reset (SSPR) for Group1. You configure security questions as the only authentication method for SSPR.
Which users can use SSPR, and which users must answer security questions to reset their password? To answer, select the appropriate options in the answer area.
NOTE; Each correct selection is worth one point.
Answer:
Explanation: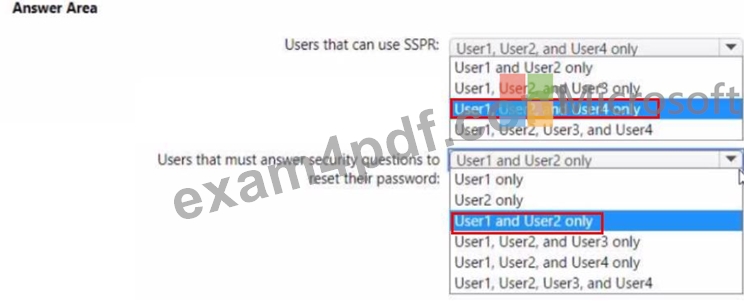
NEW QUESTION # 187
You have a Microsoft 365 E5 subscription that contains the security groups shown in the following table.
The subscription contains the users shown in the following table.
You have a Conditional Access policy that has the following settings:
* Assignments
o Users
Include: Group1
Exclude: Group2. Group3
o Target resources
Cloud apps
App1
Access controls
Grant
Block access
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 188
You have a Microsoft 365 subscription that links to an Azure Active Directory (Azure AD) tenant named contoso.onmicrosoft.com.
A user named User1 stores documents in Microsoft OneDrive.
You need to place the contents of User1's OneDrive account on an eDiscovery hold.
Which URL should you use for the eDiscovery hold? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/create-ediscovery-holds
NEW QUESTION # 189
From the Microsoft Purview compliance portal, you create a retention policy named Policy 1.
You need to prevent all users from disabling the policy or reducing the retention period.
How should you configure the Azure PowerShell command? To answer select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 190
You have a Microsoft 365 subscription that contains the users shown in the following table.
You need to configure group-based licensing to meet the following requirements:
* To all users, deploy an Office 365 E3 license without the Power Automate license option.
* To all users, deploy an Enterprise Mobility + Security E5 license.
* To the users in the research department only, deploy a Power BI Pro license.
* To the users in the marketing department only, deploy a Visio Plan 2 license.
What is the minimum number of deployment groups required?
- A. 0
- B. 1
- C. 2
- D. 3
- E. 4
Answer: B
Explanation:
Explanation
One for all users, one for the research department, and one for the marketing department.
Note: What are Deployment Groups?
With Deployment Groups, you can orchestrate deployments across multiple servers and perform rolling updates, while ensuring high availability of your application throughout. You can also deploy to servers on-premises or virtual machines on Azure or any cloud, plus have end-to-end traceability of deployed artifact versions down to the server level.
Reference:
https://devblogs.microsoft.com/devops/deployment-groups-is-now-generally-available-sharing-of-targets-and-mo
NEW QUESTION # 191
HOTSPOT
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint site named Site1 and a data loss prevention (DLP) policy named DLP1. DLP1 contains the rules shown in the following table.
Site1 contains the files shown in the following table.
Which policy tips are shown for each file? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Box 1: Rule1 tip only
File1 matches Rule1, Rule2, and Rule3.
Rule1 has the highest priority.
Note: The Priority parameter specifies a priority value for the policy that determines the order of policy processing. A lower integer value indicates a higher priority, the value 0 is the highest priority, and policies can't have the same priority value.
Box 2: Rule1 tip only
Note: User Override support
The option to override is per rule, and it overrides all of the actions in the rule (except sending a notification, which can't be overridden).
It's possible for content to match several rules in a DLP policy or several different DLP policies, but only the policy tip from the most restrictive, highest-priority rule will be shown (including policies in Test mode). For example, a policy tip from a rule that blocks access to content will be shown over a policy tip from a rule that simply sends a notification. This prevents people from seeing a cascade of policy tips.
If the policy tips in the most restrictive rule allow people to override the rule, then overriding this rule also overrides any other rules that the content matched.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/compliance/dlp-overview-plan-for-dlp
https://learn.microsoft.com/en-us/microsoft-365/compliance/use-notifications-and-policy-tips
NEW QUESTION # 192
You have a Microsoft 365 E5 tenant that connects to Microsoft Defender for Endpoint.
You have devices enrolled in Microsoft Intune as shown in the following table.
You plan to use risk levels in Microsoft Defender for Endpoint to identify whether a device is compliant.
Noncompliant devices must be blocked from accessing corporate resources.
You need to identify which devices can be onboarded to Microsoft Defender for Endpoint, and which Endpoint security policies must be configured.
What should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Text, table Description automatically generated with medium confidence
Reference:
https://docs.microsoft.com/en-us/microsoft-365/security/defender-endpoint/configure-machines-onboarding?view
NEW QUESTION # 193
You have a Microsoft 365 subscription that contains a Microsoft SharePoint Online site named Site1. Site1 has he files in the following table.
The Site1 users are assigned the roles shown in the following table.
You create a data less prevention (DLP) policy names Policy1 as shown in the following exhibit.
How many files will be visible to user1 and User2 after Policy' is applied to answer, selected select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 194
You have an Azure AD tenant and a Microsoft 365 E5 subscription. The tenant contains the users shown in the following table.
You plan to implement Microsoft Defender for Endpoint.
You verify that role-based access control (RBAC) is turned on in Microsoft Defender for Endpoint.
You need to identify which user can view security incidents from the Microsoft 365 Defender portal.
Which user should you identify?
- A. User3
- B. User2
- C. User4
- D. User1
Answer: D
NEW QUESTION # 195
You have a Microsoft 365 E5 subscription.
You need to configure a group naming policy.
Which portal should you use, and to which types of groups will the policy apply? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 196
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
Each user has an Android device with the Microsoft Authenticator app installed and has set up phone sign-in.
The subscription has the following Conditional Access policy:
* Name: Policy1
* Assignments
o Users and groups: Group1, Group2
o Cloud apps or actions: All cloud apps
* Access controls
o Grant Require multi-factor authentication
* Enable policy: On
From Microsoft Authenticator settings for the subscription, the Enable and Target settings are configured as shown in the exhibit. (Click the Exhibit tab.)
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 197
HOTSPOT
You have a Microsoft 365 E5 subscription that contains the users shown in the following table.
You plan to provide User4 with early access to Microsoft 365 feature and service updates.
You need to identify which Microsoft 365 setting must be configured, and which user can modify the setting.
The solution must use the principle of least privilege.
What should you identify? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 198
You have a Microsoft 365 E5 subscription that contains a Microsoft SharePoint Online site named Site1.
You need to automatically label the documents on Site1 that contain credit card numbers.
Which three actions should you perform in sequence? To answer, move the appropriate actions from the list of actions to the answer area and arrange them in the correct order.
Answer:
Explanation:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels?view=o365-worldwide#what- label-policies-can-do
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365- worldwide
NEW QUESTION # 199
Note: This section contains one or more sets of questions with the same scenario and problem. Each question presents a unique solution to the problem. You must determine whether the solution meets the stated goals.
More than one solution in the set might solve the problem. It is also possible that none of the solutions in the set solve the problem.
After you answer a question in this section, you will NOT be able to return. As a result, these questions do not appear on the Review Screen.
You have a Microsoft 365 E5 subscription and use Microsoft Defender for Office 365.
You need to implement a threat policy that will apply a balanced baseline protection profile to protect against spam, phishing, and malware.
Solution: You create a Strict preset security policy.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
NEW QUESTION # 200
Note: This question is part of a series of questions that present the same scenario. Each question in the series contains a unique solution that might meet the stated goals. Some question sets might have more than one correct solution, while others might not have a correct solution.
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
Your network contains an on-premises Active Directory domain named contoso.com. The domain contains the users shown in the following table.
The domain syncs to an Azure AD tenant named contoso.com as shown in the exhibit. (Click the Exhibit tab.)
User2 fails to authenticate to Azure AD when signing in as [email protected].
You need to ensure that User2 can access the resources in Azure AD.
Solution: From the Microsoft Entra admin center, you assign User2 the Security Reader role. You instruct User2 to sign in as [email protected].
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Explanation
This is not a permissions issue so you do not need to assign the Security Reader role.
The on-premises Active Directory domain is named contoso.com. User2 could sign on as [email protected] but you would first need to change the UPN of User2 to [email protected].
NEW QUESTION # 201
You need to configure a conditional access policy to meet the compliance requirements.
You add Exchange Online as a cloud app.
Which two additional settings should you configure in Policy1? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
Suggested answer:
References:https://docs.microsoft.com/en-us/intune/create-conditional-access-intune
NEW QUESTION # 202
You have a Microsoft 365 tenant that contains two groups named Group1 and Group2.
You need to prevent the members or Group1 from communicating with the members of Group2 by using Microsoft Teams. The solution must comply with regulatory requirements and must not affect other user in the tenant.
What should you use?
- A. moderated distribution groups
- B. information barriers
- C. administrator units in Azure Active Directory (Azure AD)
- D. communication compliance policies
Answer: B
NEW QUESTION # 203
HOTSPOT
You have a Microsoft 365 E5 subscription.
You need to meet the following requirements:
Automatically encrypt documents stored in Microsoft OneDrive and SharePoint.
Enable co-authoring for Microsoft Office documents encrypted by using a sensitivity label.
Which two settings should you use in the Microsoft Purview compliance portal? To answer, select the appropriate settings in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Box 1: Information protection
Automatically encrypt documents stored in Microsoft OneDrive and SharePoint.
How to integrate Microsoft Purview Information Protection with Defender for Cloud Apps Enable Microsoft Purview Information Protection All you have to do to integrate Microsoft Purview Information Protection with Defender for Cloud Apps is select a single checkbox. By enabling automatic scan, you enable searching for sensitivity labels from Microsoft Purview Information Protection on your Office 365 files without the need to create a policy. After you enable it, if you have files in your cloud environment that are labeled with sensitivity labels from Microsoft Purview Information Protection, you'll see them in Defender for Cloud Apps.
To enable Defender for Cloud Apps to scan files with content inspection enabled for sensitivity labels:
In the Microsoft 365 Defender portal, select Settings. Then choose Cloud Apps. Then go to Information Protection -> Microsoft Information Protection.
Note: Encryption of data at rest
Encryption at rest includes two components: BitLocker disk-level encryption and per-file encryption of customer content.
BitLocker is deployed for OneDrive for Business and SharePoint Online across the service. Per-file encryption is also in OneDrive for Business and SharePoint Online in Microsoft 365 multi-tenant and new dedicated environments that are built on multi-tenant technology.
Box 2: Settings
Enable co-authoring for Microsoft Office documents encrypted by using a sensitivity label.
1. Sign in to the Microsoft Purview compliance portal as a global admin for your tenant.
2. From the navigation pane, select Settings > Co-authoring for files with sensitivity files.
3. On the Co-authoring for files with sensitivity labels page, read the summary description, prerequisites, and what to expect.
4. Then select Turn on co-authoring for files with sensitivity labels, and Apply.
5. Wait 24 hours for this setting to replicate across your environment before you use this new feature for co-authoring.
Reference:
https://learn.microsoft.com/en-us/defender-cloud-apps/azip-integration
https://learn.microsoft.com/en-us/microsoft-365/compliance/sensitivity-labels-coauthoring
NEW QUESTION # 204
You have a Microsoft Azure Active Directory (Azure AD) tenant named Contoso.com.
You create a Microsoft Defender for identity instance Contoso.
The tenant contains the users shown in the following table.
You need to modify the configuration of the Defender for identify sensors.
Solutions: You instruct User1 to modify the Defender for identity sensor configuration.
Does this meet the goal?
- A. No
- B. Yes
Answer: B
NEW QUESTION # 205
Your on-premises network contains an Active Directory domain and a Microsoft Endpoint Configuration Manager site.
You have a Microsoft 365 E5 subscription that uses Microsoft Intune.
You use Azure AD Connect to sync user objects and group objects to Azure Directory (Azure AD) Password hash synchronization is disabled.
You plan to implement co-management.
You need to configure Azure AD Connect and the domain to support co-management.
What should you do? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 206
HOTSPOT
You have a Microsoft 365 E5 subscription that contains the groups shown in the following table.
All the groups are deleted.
Which groups can be restored, and what is the retention period? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
Box 1: Group3 only
Box 2: 30 days
If you've deleted a group, it will be retained for 30 days by default. This 30-day period is considered a
"soft-delete" because you can still restore the group. After 30 days, the group and its associated contents are permanently deleted and cannot be restored.
Reference:
https://learn.microsoft.com/en-us/microsoft-365/admin/create-groups/restore-deleted-group
NEW QUESTION # 207
You need to configure the Office 365 service status notifications and limit access to the service and feature updates. The solution must meet the technical requirements.
What should you configure in the Microsoft 365 admin center? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation
NEW QUESTION # 208
You have device compliance policies shown in the following table.
The device compliance state for each policy is shown in the following table.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 209
......
Download Free Microsoft MS-102 Real Exam Questions: https://www.exam4pdf.com/MS-102-dumps-torrent.html
MS-102 Exam Dumps, MS-102 Practice Test Questions: https://drive.google.com/open?id=1-OJ19AB2LNQxVJCPuQuWmWKkzfAwQw7G
